Managed SOC Services India for BFSI: Costly Gaps in Security Visibility
Why Managed SOC Services India Matter for BFSI Organisations
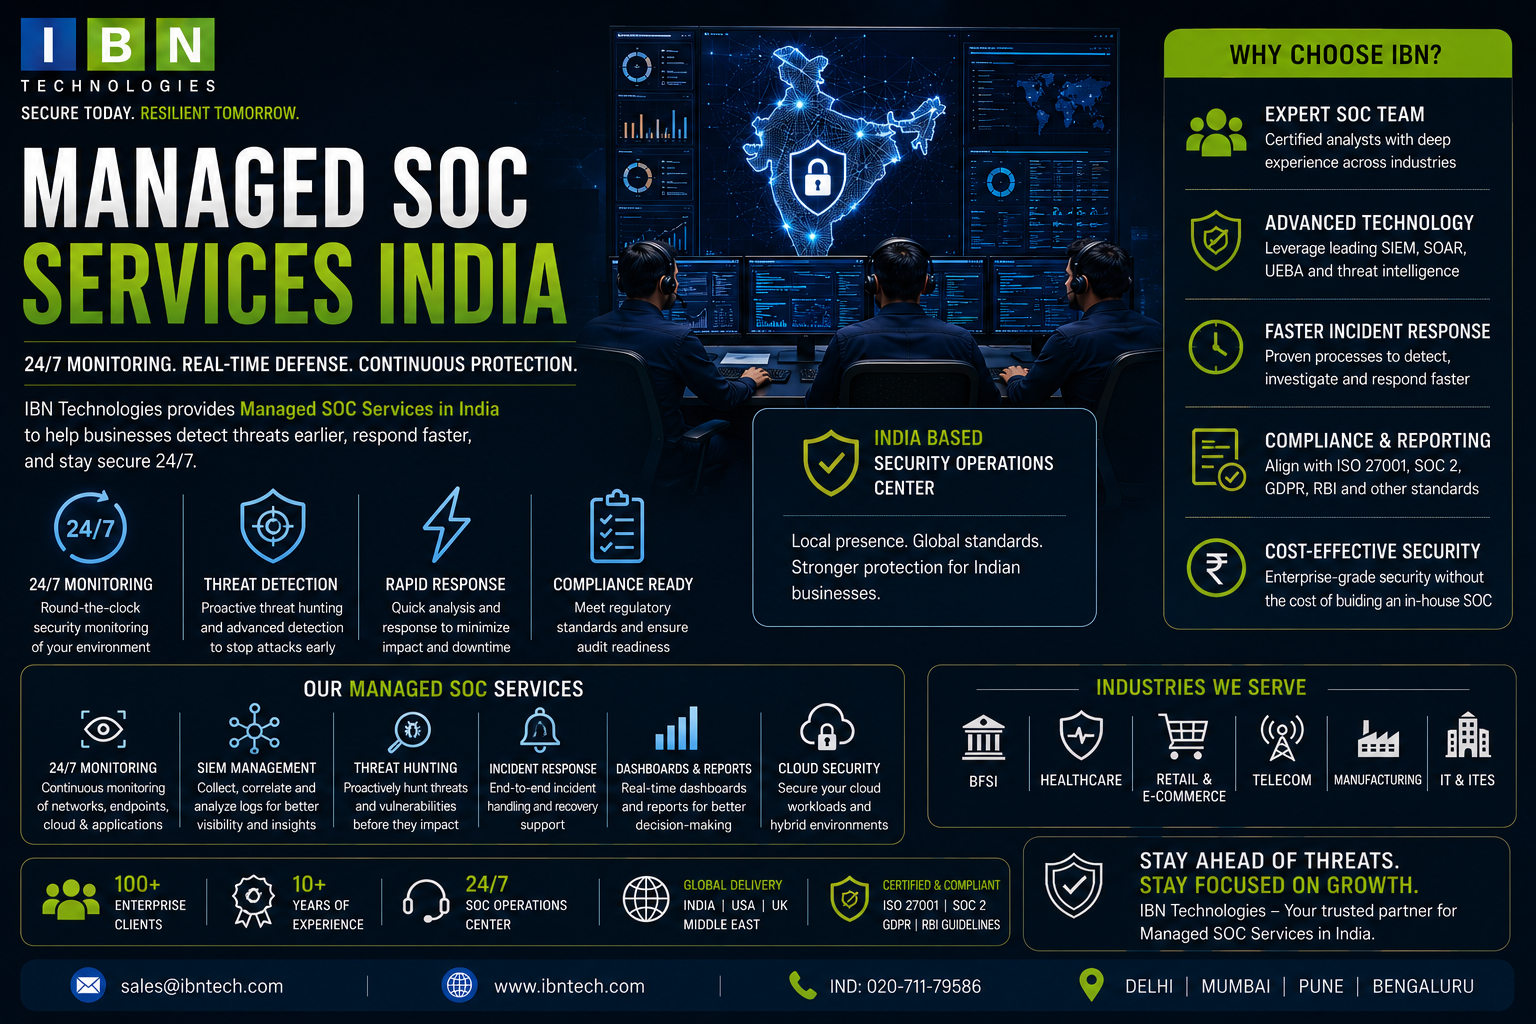
Banks, financial institutions, insurance businesses, and other BFSI organisations operate technology environments where security events can emerge across applications, networks, endpoints, user accounts, and digital services. The volume and variety of these events can make manual security monitoring difficult to sustain. managed soc services india provide a structured security operations model for monitoring, analysing, investigating, and escalating potentially significant activity.
In practical terms, managed SOC services can help BFSI security teams move from simply receiving security alerts to establishing an organised process for understanding those alerts and determining which events require further attention.
For BFSI organisations, this distinction is important because security visibility is closely connected with operational continuity, customer trust, access management, and regulatory expectations.
When Does a Managed SIEM Service Add Value to BFSI Monitoring?
A managed siem service can support the collection and analysis of security-related events from multiple technology sources. Instead of requiring security teams to manually examine disconnected event streams, SIEM capabilities can help bring relevant information together for analysis.
Within a BFSI environment, this can be useful when security activity needs to be examined across several systems. Authentication events, network activity, application behaviour, endpoint events, and other security signals may each provide only part of the picture.
The SOC operating function adds an important human and procedural layer by helping analyse alerts, investigate suspicious activity, prioritise events, and escalate matters according to defined processes.
What Makes Security Visibility Difficult in BFSI?
BFSI environments often contain multiple technology layers supporting different business functions. Security teams therefore need to understand activity across a broad environment rather than concentrating on one system.
A single alert does not always indicate a serious security event. Similarly, an apparently minor event can become more significant when combined with other related activity.
For example, repeated authentication failures followed by successful access from an unusual location may require additional investigation. When security events are correlated and reviewed within an organised monitoring process, analysts can examine the broader sequence rather than treating every notification as an isolated occurrence.
This is where managed SOC services India can provide operational support beyond basic alert generation.
How Managed SOC Services India Connect Monitoring With Investigation
Security monitoring is only one part of an effective SOC operation. The next step is determining what an alert means.
A structured managed SOC process can involve:
- Collecting relevant security events from connected environments.
- Analysing alerts according to defined detection and investigation processes.
- Prioritising events based on their potential relevance and urgency.
- Investigating suspicious activity using available contextual information.
- Escalating significant findings to the appropriate internal stakeholders.
- Supporting response coordination according to agreed responsibilities.
This process helps create a connection between security visibility and operational decision-making.
For BFSI organisations, clearly defined escalation procedures are particularly important because security teams may need to coordinate with infrastructure, application, risk, compliance, and business stakeholders.
Why BFSI Teams Should Look Beyond SIEM Technology Alone
A SIEM platform can provide valuable security visibility, but technology alone does not determine how effectively an organisation responds to security events.
Security teams also need processes for reviewing alerts, investigating unusual activity, managing escalation, and documenting relevant findings.
This means organisations evaluating a managed siem service should consider how the technology fits into the wider security operations model.
Questions worth examining include:
- What security data can be monitored?
- How are alerts prioritised?
- What investigation processes are followed?
- How are false positives handled?
- When is an event escalated?
- Who receives security notifications?
- What responsibilities remain with the internal team?
- How are monitoring activities documented?
These factors help distinguish a technology-focused deployment from an operationally supported security monitoring approach.
Benefits of Managed SOC Services for BFSI Security Operations
A managed SOC model can support BFSI organisations in several practical areas.
- Centralised security visibility: Relevant security events can be examined through an organised monitoring function.
- Alert analysis: Security notifications can be assessed instead of relying solely on automated alerts.
- Faster escalation: Defined processes can help route significant events to responsible stakeholders.
- Investigation support: Suspicious activity can receive structured analysis and contextual review.
- Operational consistency: Monitoring and investigation can follow established procedures.
- Security team support: Internal teams can receive additional operational capacity without transferring every security responsibility externally.
The effectiveness of these benefits depends on the organisation's technology environment, monitoring scope, processes, and division of responsibilities.
A BFSI Scenario: From Isolated Alert to Security Investigation
Consider a financial organisation with multiple digital applications and user access systems.
An unusual authentication event is detected. On its own, the event may not provide enough information to determine its significance. Additional events later show unusual activity involving another system.
When these events are viewed together, the security team has more context for investigation. Analysts can review the sequence, assess its relevance, and determine whether escalation is required.
The managed SOC can support the monitoring and investigation process, while the BFSI organisation retains control over business decisions and approved response actions.
This model illustrates why security visibility should be considered an ongoing operational capability rather than simply a collection of security alerts.
A Practical Evaluation Checklist for BFSI Organisations
Before adopting managed SOC services India, BFSI organisations should evaluate:
- Systems and applications that require security monitoring
- Security event sources available for analysis
- SIEM capabilities and integration requirements
- Alert prioritisation procedures
- Investigation workflows
- Escalation and communication processes
- Internal and external security responsibilities
- Monitoring coverage requirements
- Reporting and documentation expectations
- Governance and compliance requirements
A clearly defined scope can help prevent gaps between the managed security operation and the organisation's internal security processes.
Compliance and Security Governance in BFSI
Security monitoring should operate alongside broader governance and compliance controls. BFSI organisations need to consider their applicable regulatory obligations, internal policies, access controls, risk processes, and information-security requirements.
For organisations working toward or maintaining frameworks such as ISO 27001, security monitoring and incident-management processes can form part of a broader control environment. The exact requirements depend on the organisation, its activities, and applicable regulations.
A managed SOC should therefore be integrated into the organisation's overall security governance rather than treated as an isolated technical service.
BFSI security operations increasingly depend on the ability to identify meaningful activity within large volumes of security data. managed soc services india can provide an organised approach to monitoring, alert analysis, investigation, and escalation, while a managed SIEM capability can help strengthen the underlying security-event visibility. For BFSI organisations, the value comes from connecting technology, people, processes, and defined responsibilities into a consistent security operations model.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - sales@ibntech.com

 English
 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Greek