SOC SIEM Consulting for Indian BFSI: An Essential Security Governance Guide
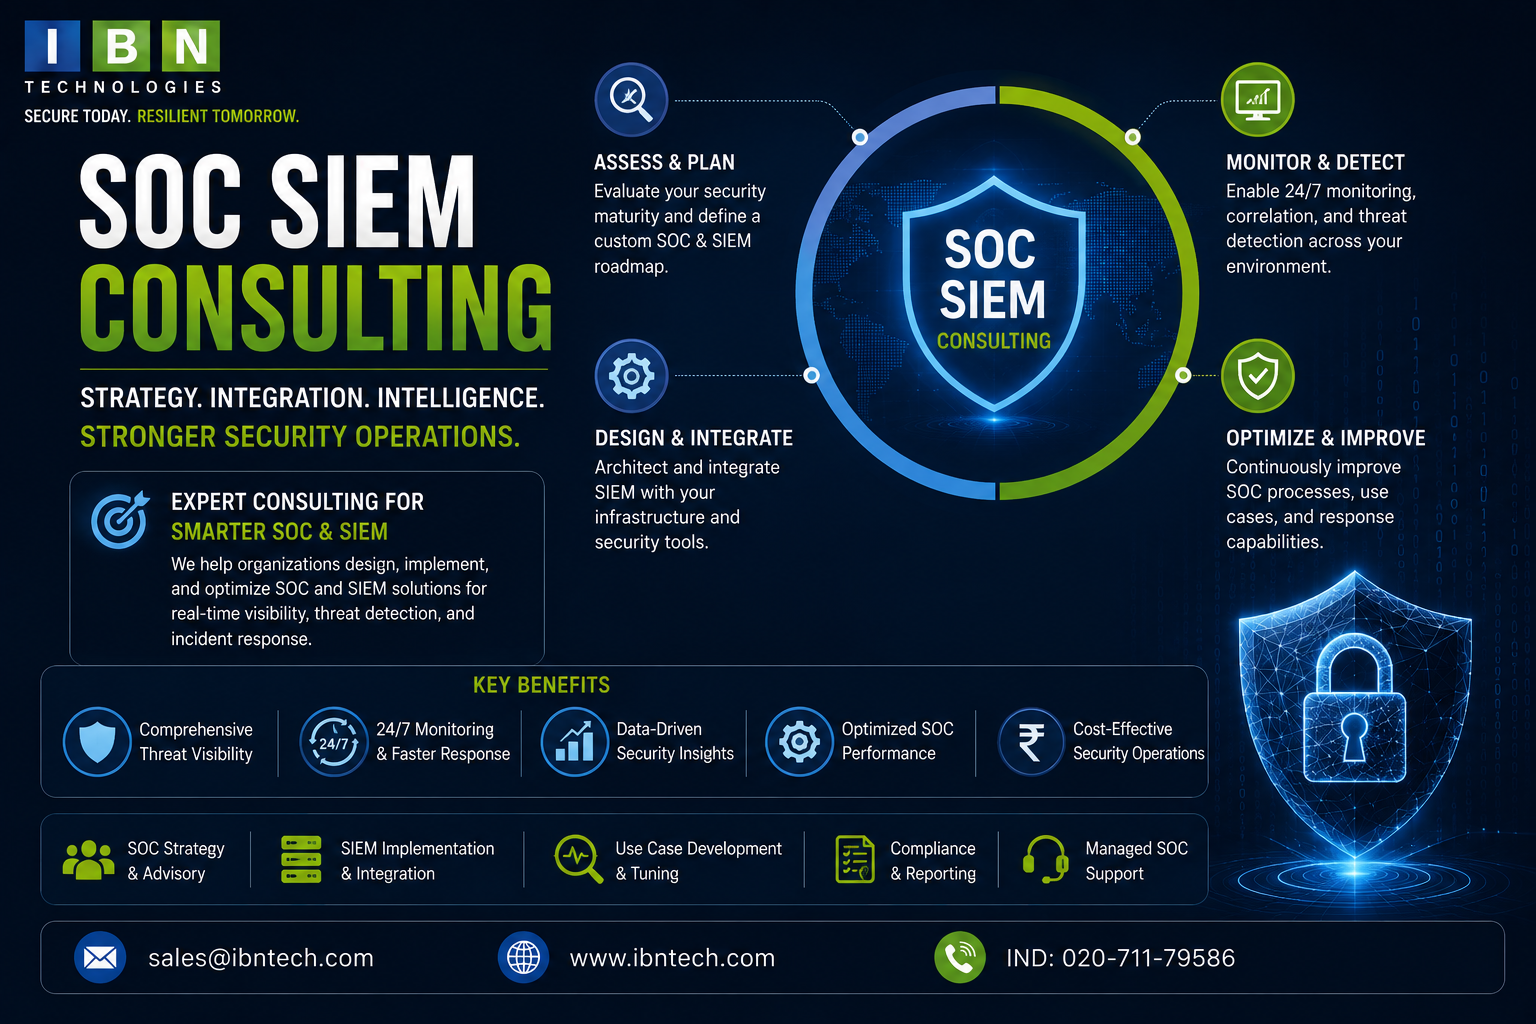
Where BFSI Security Operations Meet Smarter SOC SIEM Consulting
Financial institutions operate in an environment where digital transactions, customer information, internal applications, authentication systems, and connected infrastructure must work reliably while remaining protected.
For BFSI organizations, cybersecurity monitoring is therefore closely connected with operational continuity, information protection, governance, and regulatory expectations.
soc siem consulting can help BFSI security teams examine whether their monitoring and security operations are aligned with the organization's actual environment. Rather than treating SIEM as simply a log collection platform, consulting can help establish how security information should be collected, analyzed, investigated, escalated, and reported.
For Indian BFSI organizations, this alignment is particularly important because security operations need to support both technology environments and the governance processes surrounding them.
Why SOC SIEM Consulting Matters in BFSI
SOC SIEM consulting provides a structured way to assess and improve security monitoring, detection, investigation, and response capabilities.
In BFSI, the objective is not simply to identify suspicious activity. Security teams also need sufficient context to understand what happened, determine whether further investigation is necessary, and coordinate an appropriate response.
SIEM technology can bring relevant security events together, while SOC operations provide monitoring and analytical processes around those events.
This combination can help organizations develop a clearer security operating model. It can also support better coordination between cybersecurity teams, IT operations, risk functions, and relevant business stakeholders.
For BFSI institutions, that coordination matters because security events may involve systems with direct operational or customer impact.
The Role of a Managed SOC Provider in BFSI Security
A managed soc provider can support BFSI organizations that require external security monitoring expertise or want to extend their existing security operations capabilities.
The relationship should be defined around the organization's actual security requirements. Monitoring scope, escalation procedures, incident investigation, reporting, responsibilities, and service coverage should be understood before the operating model is implemented.
For a financial organization, this clarity becomes especially important during a potential security incident. The organization should know who investigates the event, who communicates internally, who coordinates technical remediation, and how the incident is documented.
External monitoring can supplement internal capabilities, but organizational ownership of security decisions and business processes still needs to remain clear.
BFSI Security Is About More Than Detecting Alerts
A financial institution can generate security events from many parts of its technology environment.
Authentication activity, endpoint events, network behavior, application activity, privileged access, and other relevant systems can contribute to the overall security picture.
Looking at these events independently may make it harder to identify relationships between them.
For example, an unusual authentication event may require a different level of attention depending on what happens before or after it. When related security events can be correlated, analysts may have more context for deciding whether an investigation is warranted.
SIEM capabilities can support this correlation, but the effectiveness of the monitoring process also depends on appropriate data sources, detection logic, analyst investigation, and response procedures.
Why Traditional Monitoring Models Can Create Gaps
One challenge for BFSI organizations is the assumption that deploying security technologies automatically creates effective monitoring.
Technology can collect events, but organizations still need to decide which events matter, how they should be analyzed, and what happens when suspicious activity is detected.
Another challenge is fragmented visibility.
Different teams may operate different security tools or infrastructure platforms. If important information remains isolated, analysts may have to manually connect events across multiple systems.
Staffing can create another operational consideration. Security monitoring requires trained personnel and defined processes. Maintaining sufficient coverage internally can require ongoing investment in people, technology, and operational management.
A consulting-led assessment can help identify whether the current model is producing the visibility and response capability the organization expects.
Mapping Monitoring to BFSI Risk Priorities
Not every event deserves the same level of attention.
BFSI organizations can begin by identifying systems, accounts, applications, and processes that are particularly important to their operations. Monitoring can then be structured around relevant security scenarios and risk priorities.
This may involve considering areas such as:
- Identity and authentication activity
- Privileged account activity
- Endpoint security events
- Network-related security signals
- Critical application activity
- Suspicious access patterns
- Security control events
- Incident-related activity
The exact monitoring scope should reflect the organization's technology environment and applicable requirements.
The important principle is prioritization. Security teams should have a reason for collecting and monitoring a particular source rather than accumulating information without an operational purpose.
Building an Investigation-Ready SIEM Environment
A SIEM environment should provide useful context to analysts.
That means relevant events need to be available in a form that supports investigation. Data quality, time synchronization, source configuration, and appropriate event context can all influence how effectively security teams analyze activity.
Detection rules also require ongoing attention.
A rule that was useful when an environment was configured one way may need adjustment after systems, applications, or access patterns change.
For BFSI organizations, this creates a continuous improvement requirement. Security monitoring should evolve alongside the environment instead of being treated as a one-time implementation.
SOC SIEM consulting can help organizations identify where this operational lifecycle needs greater structure.
Incident Response Should Connect With Monitoring
Monitoring and incident response should not operate as separate functions.
When a potential security incident is identified, there needs to be a defined path from alert to investigation and from investigation to appropriate response.
That process can include alert validation, evidence gathering, escalation, containment, remediation, documentation, and post-incident review, depending on the nature of the event and the organization's established procedures.
The exact responsibilities should be agreed before an incident occurs.
A managed security model may involve external analysts identifying and investigating events while the BFSI organization's internal teams remain responsible for actions involving its infrastructure or business operations.
Clear escalation criteria help both sides understand when an event needs greater attention.
Governance Requires Evidence, Not Just Technology
Security governance is strengthened when organizations can demonstrate how controls operate in practice.
Monitoring and logging can contribute to this evidence by providing records of security activity and supporting investigation processes.
However, the presence of logs alone does not demonstrate that an organization has effective security operations.
Organizations also need defined procedures, appropriate responsibilities, documented escalation paths, and mechanisms for reviewing security events.
This is why SOC and SIEM planning should be connected with governance rather than treated purely as a technical deployment.
For Indian BFSI organizations, applicable regulatory and contractual requirements should be considered when defining security monitoring, logging, incident management, and reporting practices. RBI requirements may be relevant to regulated entities depending on the organization's specific status and obligations, while broader Indian data protection requirements may also need consideration.
Assessing a Managed Security Operating Model
BFSI organizations evaluating external SOC support can examine several practical areas.
|
Evaluation Area |
Questions to Consider |
|
Monitoring scope |
Which systems, applications, and security sources are included? |
|
Detection |
How are suspicious events identified and prioritized? |
|
Investigation |
Who validates alerts and performs deeper analysis? |
|
Escalation |
What circumstances trigger notification to internal teams? |
|
Response |
Which actions are handled by the provider and which remain internal? |
|
Reporting |
What information is provided to security, risk, and management teams? |
|
Compliance support |
Can monitoring and reporting contribute to applicable governance requirements? |
|
Change management |
How are new systems and security requirements incorporated into monitoring? |
These questions can help BFSI organizations evaluate the operating model instead of focusing only on the underlying security platform.
Security Reporting Should Serve Multiple Stakeholders
Different stakeholders require different types of information.
Security analysts may need detailed event information and investigation context. IT teams may need actionable technical findings. Risk and governance teams may need evidence about control operation and incident handling. Senior management may need a concise view of significant security activity and outstanding concerns.
A well-designed SOC reporting model can accommodate these different requirements without overwhelming every stakeholder with the same level of technical detail.
This also makes reporting more useful for governance discussions. Instead of producing reports simply because they are part of a service process, organizations can establish what decisions each report is expected to support.
Common BFSI SOC and SIEM Planning Mistakes
A frequent mistake is treating compliance as the only reason to implement security monitoring. Compliance requirements can influence monitoring, but security operations should also support real-world detection and response.
Another mistake is assuming that more logs automatically mean better visibility. Without appropriate analysis and prioritization, additional data can increase operational complexity.
Organizations can also underestimate the importance of ownership. When multiple teams or an external provider participate in security operations, unclear responsibilities can delay incident handling.
A further problem is failing to review monitoring after major technology changes. New applications, infrastructure, integrations, or authentication methods can alter the organization's security visibility.
Finally, organizations should avoid evaluating a SOC service solely on the number of alerts it processes. Meaningful security operations are concerned with identifying relevant activity, investigating it appropriately, and supporting effective response.
A Practical BFSI Security Monitoring Checklist
BFSI security teams can use the following areas as a starting point when reviewing their SOC and SIEM environment:
- Identify systems and applications requiring priority monitoring
- Map relevant security data sources
- Review the quality and completeness of collected security events
- Define meaningful detection scenarios
- Establish alert investigation procedures
- Document incident escalation responsibilities
- Clarify internal and external response ownership
- Align reporting with security and governance requirements
- Review monitoring when infrastructure changes
- Periodically assess detection effectiveness and operational gaps
- Maintain appropriate evidence for relevant security and compliance processes
This approach keeps the monitoring program connected to operational needs rather than treating it as a static technology deployment.
Creating a Sustainable Security Operations Framework
BFSI cybersecurity requires an operating model that can keep pace with changing technology and evolving security requirements.
SOC and SIEM capabilities can provide important foundations, but their effectiveness depends on how well the organization connects technology with people, processes, monitoring priorities, investigation procedures, and response responsibilities.
For Indian financial institutions, soc siem consulting can provide a structured starting point for examining these connections. It can help security teams understand where visibility exists, where gaps remain, and how the SOC and SIEM model can better support operational and governance requirements.
IBN Technologies offers SOC & SIEM services within its cybersecurity portfolio, alongside VAPT, MDR, vCISO, and Microsoft Security services. Organizations evaluating security operations support can assess these capabilities according to their specific environment and requirements.
A sustainable BFSI security model is ultimately built around clear visibility, defined accountability, meaningful detection, disciplined investigation, and a response process that connects security teams with the wider organization.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - sales@ibntech.com

 English
 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Portuguese (Brazil)
 Greek