


Managed SOC as a Service in India: A Costly Visibility Gap for BFSI
When BFSI Security Needs More Than Alerts: Managed SOC as a Service
Indian BFSI organizations operate in an environment where digital banking, financial applications, customer portals, payment systems, employee access, and interconnected infrastructure all contribute to a complex security landscape. A suspicious event in one environment can have implications elsewhere, making continuous monitoring increasingly important. managed soc as a service provides an operational security layer for monitoring activity, investigating threats, and supporting incident response.
For banks, financial institutions, and other BFSI organizations, the challenge is not merely collecting security alerts. Security teams need enough context to determine which events require investigation and how incidents should be escalated.
What does managed SOC as a service provide to BFSI organizations?
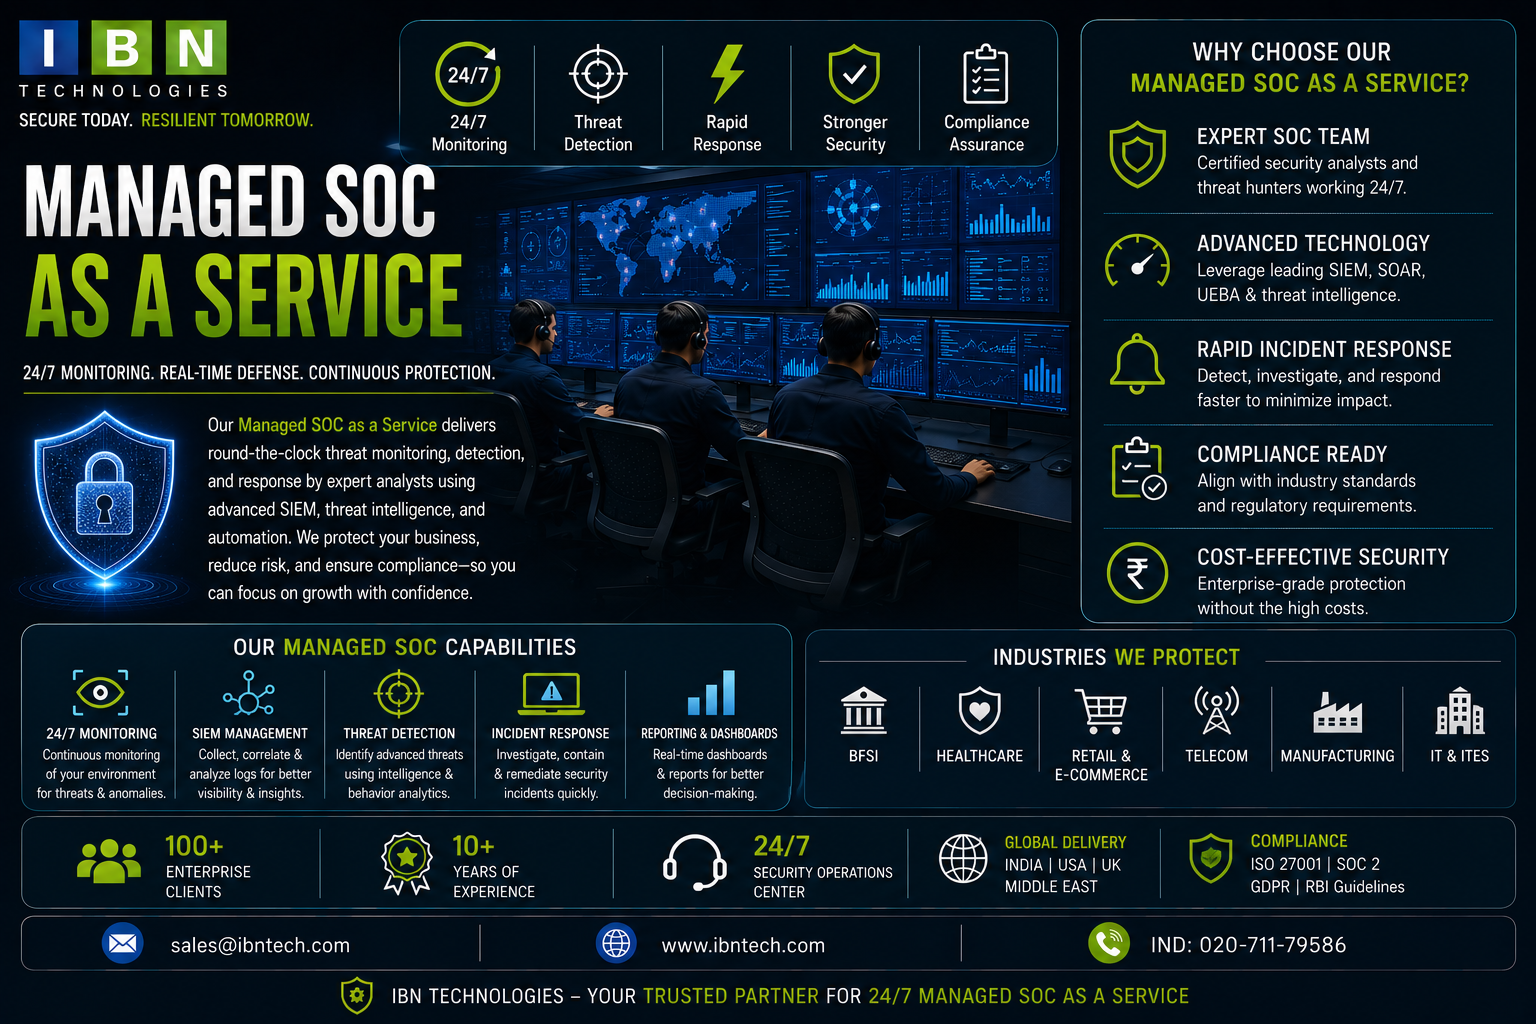
Managed SOC as a service is an outsourced security operations model that combines continuous security monitoring, threat detection, investigation, and response support. Security events from relevant systems can be monitored and analyzed by security professionals who identify suspicious activity and escalate incidents according to defined procedures.
For BFSI organizations, this approach can help connect security monitoring with operational response. Financial institutions typically manage multiple systems, users, applications, endpoints, and network environments, creating a broad security monitoring requirement.
A managed SOC does not remove the organization's responsibility for security. Instead, it can extend internal capabilities through a dedicated external monitoring and security operations function.
Why is a managed SIEM service important for BFSI security?
A financial organization can generate security information from many different systems. managed siem service capabilities can help centralize and analyze security events so that potentially related activities are easier to investigate.
SIEM technology can collect and correlate security information, while managed security operations add human analysis and operational processes around that data.
For example, an unusual login may not appear significant by itself. When combined with other suspicious events, it may provide additional context for investigation. Security analysts can examine the wider event pattern instead of treating every notification as an isolated alert.
For BFSI organizations, this combination of technology and security operations can help create a more structured approach to threat visibility.
Why are isolated security alerts a problem for financial institutions?
An alert typically represents an observation, not a complete incident assessment.
A security team needs to understand what generated the alert, whether the activity is expected, what other systems may be involved, and whether the event requires escalation.
When alerts are handled independently, the organization may have difficulty identifying broader patterns. Centralized monitoring and analysis can provide additional context for security investigations.
What security challenges make continuous monitoring important for BFSI?
Financial organizations face a wide range of security concerns, including unauthorized access, credential misuse, suspicious network activity, malware, phishing-related events, and other forms of cyber threats.
The increasing use of digital services also expands the number of systems that need to be monitored.
Internal security teams may have to balance incident monitoring with compliance activities, vulnerability management, security reviews, infrastructure changes, and other responsibilities. This can make continuous monitoring difficult when resources are limited.
A managed SOC can provide dedicated operational capacity for security monitoring and investigation while allowing internal teams to retain control over business-critical decisions and remediation.
How does managed SOC as a service support threat detection?
Managed SOC operations generally begin with collecting relevant security information from connected systems and devices.
Security events can then be analyzed for indicators of suspicious activity. Analysts can investigate unusual patterns and determine whether an event represents a legitimate business activity, a false positive, or a potential security incident.
IBN Technologies' managed SIEM and SOC services include continuous security monitoring, threat detection, threat intelligence, threat hunting, security device monitoring, incident response and forensics, user behavior analytics, and policy and compliance monitoring.
For BFSI organizations, these capabilities can support a broader security monitoring process rather than relying on a single security control.
What happens after a potential threat is detected?
The next step is investigation.
Security professionals can examine available information to understand the nature and potential significance of the event. Depending on the findings, the incident can be escalated through the organization's defined response process.
This is where operational procedures become important. The organization should know who receives critical alerts, who makes business decisions, who handles remediation, and how the incident is documented.
A clear escalation model can reduce confusion when rapid action is required.
How should BFSI organizations evaluate a managed SOC provider?
Financial institutions should assess a provider against their actual security environment and regulatory responsibilities.
Monitoring coverage is an important starting point. The provider should be able to work with the security data sources that are relevant to the organization's infrastructure.
Threat detection and investigation capabilities should also be examined. A service that only forwards alerts may provide less operational value than one that includes analysis and escalation.
Reporting is another consideration. BFSI security leaders may require clear records of incidents, monitoring activity, investigations, and response actions.
The provider's approach to compliance monitoring should also be understood, particularly where the organization has regulatory obligations.
Can managed SOC help BFSI organizations improve security governance?
Security monitoring can contribute to governance by creating an ongoing operational record of security events and responses.
For Indian BFSI organizations, applicable regulatory requirements can include expectations from bodies such as the Reserve Bank of India, depending on the organization and its regulated activities. ISO 27001 may also be relevant where organizations use the standard as part of their information security management framework.
IBN Technologies' managed security services include compliance-oriented monitoring and reporting aligned with applicable frameworks and requirements, including ISO 27001 and RBI-related requirements for relevant BFSI environments.
Compliance should not be viewed as a separate activity from security operations. Monitoring, incident management, policy enforcement, access controls, and evidence collection can all contribute to a stronger governance process.
What should financial institutions look for beyond 24/7 monitoring?
The phrase "24/7 monitoring" describes availability, but it does not explain the depth of the service.
A BFSI organization should ask how alerts are analyzed, how suspicious activity is investigated, what threat intelligence is used, how incidents are escalated, and what reporting is provided.
It is also important to understand how the managed SOC interacts with internal security and technology teams.
The service should have clearly defined procedures for communication and escalation. Critical incidents should not become delayed because ownership is unclear.
Managed SOC evaluation checklist for BFSI
- Continuous security monitoring
- SIEM-based security event analysis
- Threat detection and investigation
- Threat intelligence capabilities
- Threat hunting
- Incident escalation procedures
- Incident response and forensic support
- User behavior analytics
- Policy and compliance monitoring
- Security reporting and documentation
The exact requirements will vary between BFSI organizations, so the checklist should be adapted to the organization's infrastructure, risk environment, and regulatory responsibilities.
Frequently Asked Questions
What is managed SOC as a service in BFSI?
Managed SOC as a service provides outsourced security monitoring, threat detection, investigation, and response support for financial organizations. It can supplement internal security teams with continuous security operations capabilities.
How does managed SIEM support BFSI organizations?
A managed SIEM service can centralize and analyze security events from relevant systems, helping security teams identify patterns and investigate suspicious activity. Managed security personnel can add operational analysis and escalation around the collected information.
Does a managed SOC replace a bank's internal security team?
No. A managed SOC can complement internal teams by handling or supporting continuous monitoring, investigation, reporting, and escalation while internal personnel retain organizational responsibilities and decision-making authority.
Can managed SOC support regulatory security requirements?
Managed SOC operations can support security monitoring, documentation, reporting, and compliance processes. The specific regulatory requirements applicable to a BFSI organization depend on its activities and the regulations governing it.
For BFSI organizations, security visibility needs to extend beyond individual alerts. managed soc as a service can combine continuous monitoring, SIEM-driven analysis, threat detection, investigation, and response support into a structured security operations model.
As Indian financial organizations continue expanding digital operations, the ability to identify and investigate suspicious activity across interconnected environments becomes increasingly important. A managed SOC can serve as an extension of internal security operations when its monitoring scope, escalation model, reporting, and compliance support are aligned with the organization's requirements.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - sales@ibntech.com

 English
 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Portuguese (Brazil)
 Greek